Turn Microsoft Defender alerts into action, right inside Microsoft Teams
Micro-Vigilant brings Microsoft Defender incidents and alerts into Microsoft Teams, with role-based views, smart notifications and actions your team can take from the notification itself, with full traceability.


The gap is not the tools. It is operations.
Microsoft Defender detects and prioritizes. Every alert still needs an owner, the business context and a next step, and that is where security teams run out of time.
of alerts still go uninvestigated, even with Microsoft Defender XDR and Microsoft Sentinel deployed.
Microsoft & Omdia, State of the SOC (2026)of cybersecurity spend goes to people and operations. Tools alone are 35–40%.
Forrester, Gartner, IDC, IBM (2024)days to identify a breach, out of a 240-day breach lifecycle.
IBM, Verizon, ENISA, Ponemon and others (2023–2025)Five capabilities, one operational experience
Operate
- Microsoft Defender incidents and alerts, centralized in Microsoft Teams with no portal switching.
- Role-based views for analysts, managers and admins, focused on relevant signals.
Manage
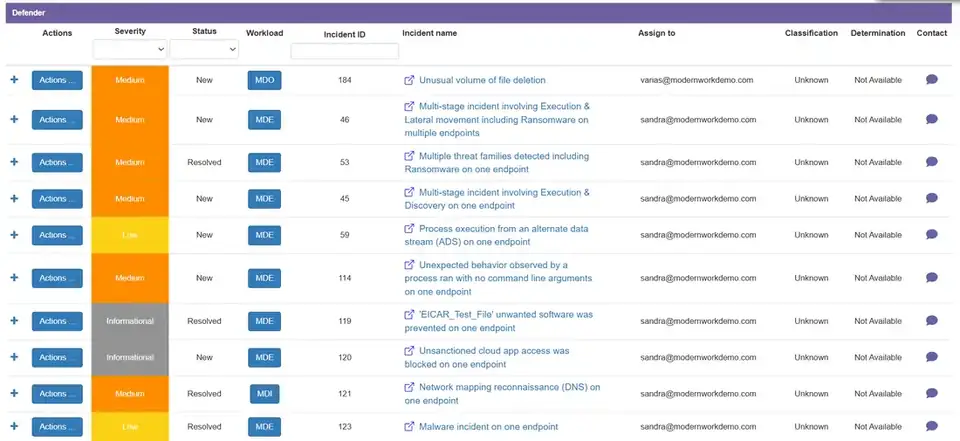
- Clear visibility of the incidents and alerts assigned to each analyst.
- Central configuration of notifications, automation and AI, beyond assignment.
Notify
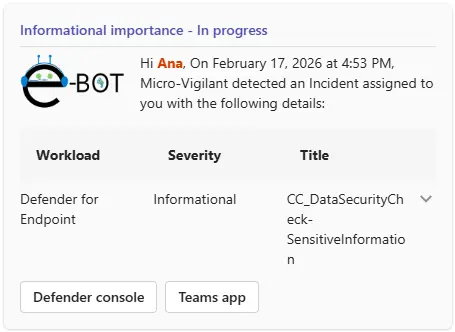
- Structured, contextual alerts prioritized by what matters to the business.
- Follow-up reminders that keep incidents moving and reduce alert fatigue.
Automate
- Predefined actions for specific alerts and incidents.
- Less repetitive manual work and consistent, timely responses.
AI assist & agentic
- Incident context for technical and executive audiences.
- What happened, its impact and the recommended actions, in a concise summary.
Your Defender operations, in one Teams app
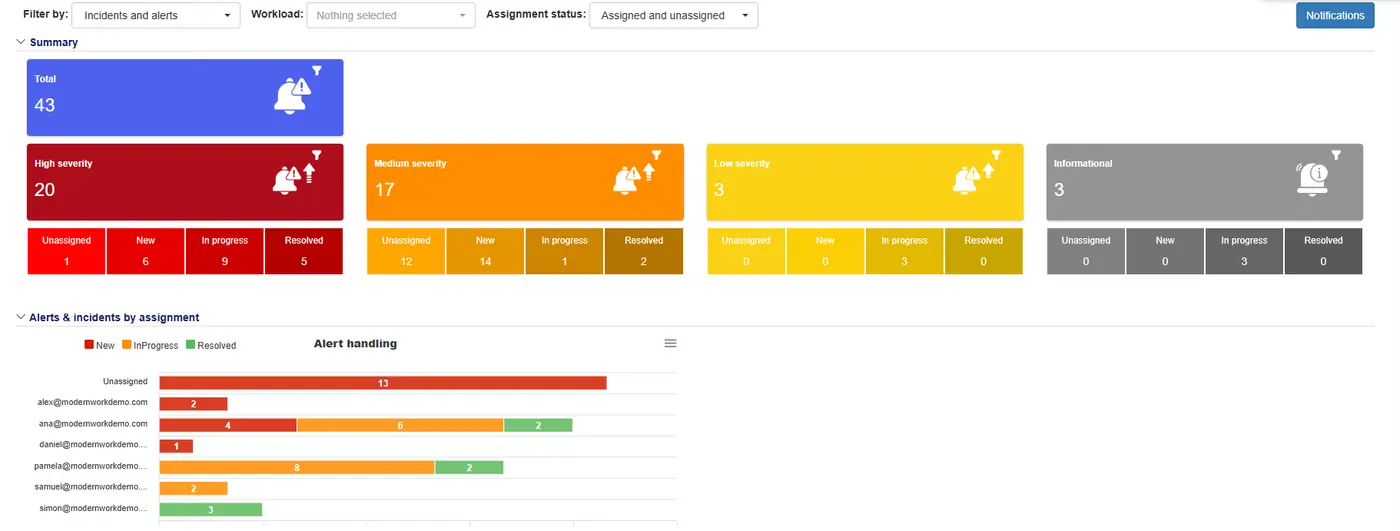
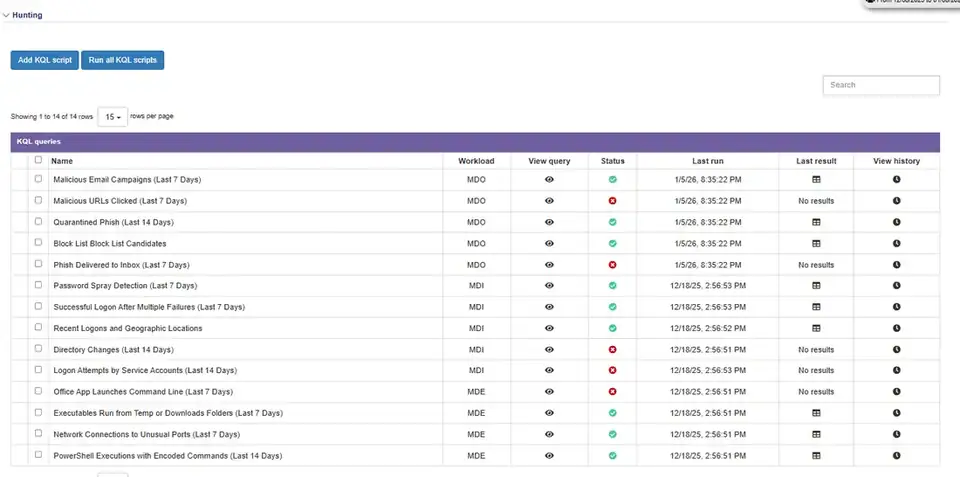
Summary, incidents, hunting and notifications, in a single app pinned in Microsoft Teams and accessible from any device.


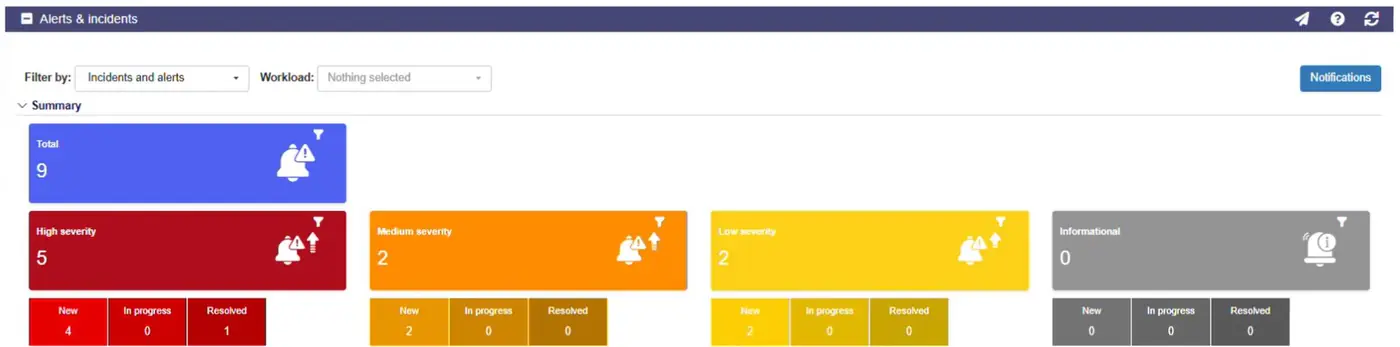
Incidents and alerts by severity, status and analyst, at a glance.
From Microsoft Defender to action
Micro-Vigilant reads incidents and alerts through Microsoft Graph API, filters them by workload, severity, status and frequency, and delivers them where your team already works.

The solution runs inside your tenant, with data provided directly by Microsoft through Microsoft Graph, so sensitive data does not leave your organization.
The right view for every role
Managers govern the operation. Analysts focus on the incidents assigned to them.
Visibility, control and governance

Triage, investigation and response

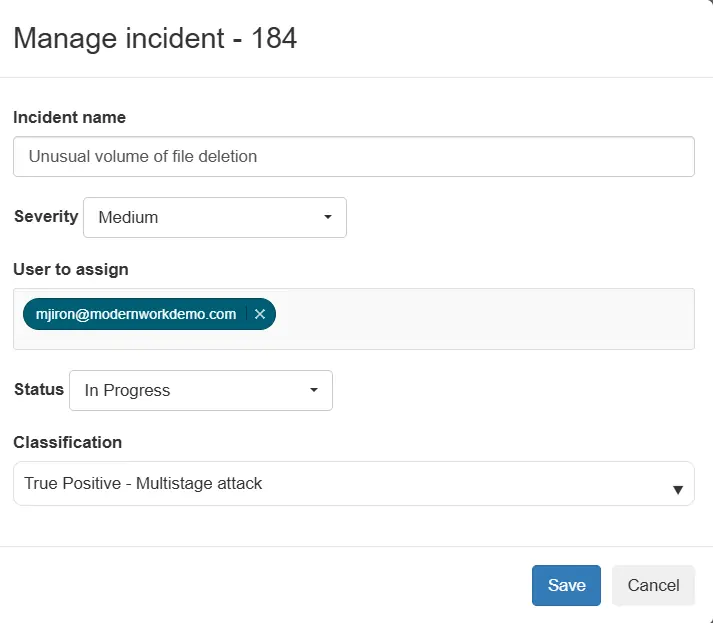
Approve, act and prove it
Guided actions and safe automated execution, with approvals where they matter and an audit trail for every step.
Incident context, in plain language
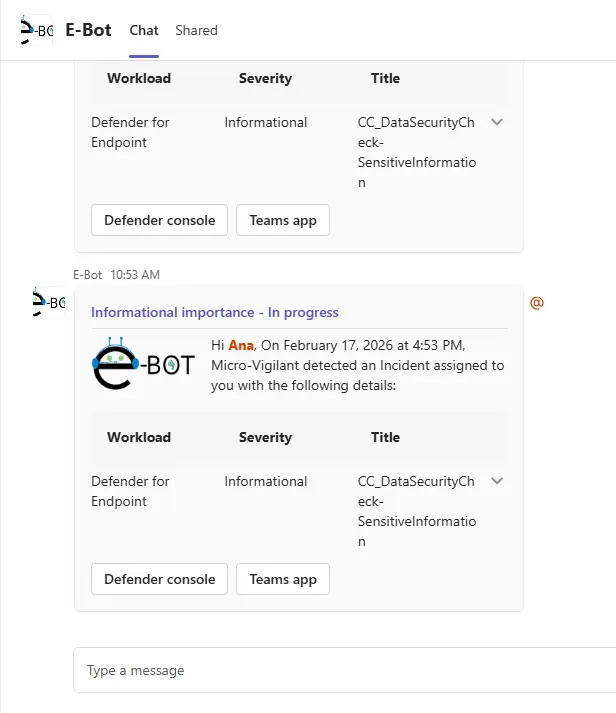
With Microsoft Security Copilot, Micro-Vigilant adds incident summaries, enrichment and insights to the notifications your team receives in Microsoft Teams: what happened, why it matters and what to do next.
- Incident summaries for technical and executive audiences
- Enrichment of the users and devices involved
- Recommended next steps, inside the notification
Copilot-assisted capabilities require Microsoft Security Copilot and/or Microsoft 365 E5.
Suspected brute-force attack on a user account
Repeated failed sign-ins from two unfamiliar locations were followed by a successful sign-in on the same account.
The account has access to finance data, so a compromise could expose sensitive information.
Revoke active sessions, force a password reset and review recent mailbox rules.
One app across Microsoft Defender
Examples of how security teams use Micro-Vigilant in each Defender workload.
Vulnerability remediation
- Critical exposure flagged in Teams
- Owner assigned by business criticality
- Weekly reminders until it is fixed
Account compromise response
- Identity incident with evidence in Teams
- IT approves disable user and reset password
- User ID and timestamp logged
Quarantine release
- Verified false positive reported
- Owner and second validator approve
- Message released with before/after evidence
Cloud app governance
- Monthly review shortcut in Teams
- Policies tuned and noisy rules disabled
- Risky OAuth apps suspended after approval
Time, cost, risk and optimization
Faster response and lower MTTR
- Response actions directly from Teams: isolation, scans, restrictions
- Reminders that prevent delays in handling and follow-up
Lower operational overhead
- Less manual effort through automation and role-based workflows
- Operations centralized in Teams, with less tool sprawl and training
Reduced exposure, stronger governance
- Faster remediation and patching shrink the attack surface
- Role-based workflows with full auditability
Simpler, consistent operations
- Standardized SOC workflows improve consistency
- Notifications, investigation and action in one place
Choose how you acquire Micro-Vigilant
Microsoft Marketplace
A transactable offer in Microsoft Marketplace. Micro-Vigilant is MACC eligible, so the purchase can count toward your Azure consumption commitment.
Directly from Synergy Advisors
For organizations that want commercial and technical guidance from our experts during adoption.
Through partners
Available from authorized partners through the Microsoft Marketplace partner-to-partner model.
Trial
Evaluate Micro-Vigilant in your environment before a full acquisition.
Frequently asked questions
What is Micro-Vigilant?
Micro-Vigilant is a Synergy Advisors E-Suite solution that brings Microsoft Defender incident and alert operations into Microsoft Teams. It gives analysts and managers role-based views, smart notifications and actions they can take from Teams, with full traceability and auditing.
Which Microsoft Defender workloads does it cover?
Microsoft Defender for Endpoint, Microsoft Defender for Identity, Microsoft Defender for Office 365 and Microsoft Defender for Cloud Apps.
Where does Micro-Vigilant run?
The solution is deployed inside your own tenant and receives data directly from Microsoft through Microsoft Graph, so sensitive data does not leave your organization.
Which actions can my team take from Microsoft Teams?
Depending on your configuration and existing automations: isolate a machine, run a quick or full scan, restrict app execution, disable a user, reset a password, close active sessions, block a sender, release a verified false positive and suspend an OAuth app. Every action is verified and logged.
How are people notified?
Through the Micro-Vigilant chatbot, 1:1 chats and channels in Microsoft Teams, with e-mail as a complementary channel. Notifications can be filtered by workload, severity and status, and delivered immediately, daily or weekly.
Does it work with Microsoft Security Copilot?
Yes. With Microsoft Security Copilot and/or Microsoft 365 E5, Micro-Vigilant adds incident summaries, enrichment and insights to the notifications in Teams.
How can we acquire it?
Through Microsoft Marketplace, where Micro-Vigilant is MACC eligible, directly from Synergy Advisors, or through authorized partners. A trial is available.
What do we need to use it?
Microsoft Defender in your tenant and a Microsoft Teams license for each analyst or manager who uses the app.
You may also need
Micro-Vigilant SecOps Agent
AI agent that measures SOC performance, workload and detection quality from Defender XDR data.
E-Vigilant
Business-driven alerts, notifications and workflows for security, compliance and productivity events.
MXDR managed security
24x7x365 monitoring, hunting and response across Microsoft Defender XDR and Microsoft Sentinel.
Talk to our Micro-Vigilant experts
Tell us about your security operations. A Synergy Advisors specialist will show you Micro-Vigilant on the Defender incidents that matter to you.
Share your contextYour Defender workloads, team and priorities.
See it workingA demo on the scenarios that matter to your team.
Get startedIn English or Spanish, with our experts alongside you.