
E-gents: AI agents for Microsoft security and identity
E-gents are the Synergy Advisors AI agents for the Microsoft platform. Each one does one job for one team, from identity administrators to every employee and the SOC, and answers in plain language from your own Microsoft data.
One agent, one job
A general assistant answers a bit of everything. Each E-gent is built around one team and one outcome, with the data that job needs.
Built for one team
Identity administrators, every employee or the SOC: each agent knows its audience and the questions it asks.
Your own Microsoft data
Answers come from your Microsoft Entra ID or Microsoft Defender XDR data, not from generic examples.
Plain language
Ask the way you would ask a colleague and get a direct answer, with no report to build.
Where your team works
Microsoft Teams, Copilot Studio and Microsoft Security Copilot. Nothing new to learn.
Meet the E-gents
Real screenshots of each agent at work. Every agent has its own page with the details and requirements.
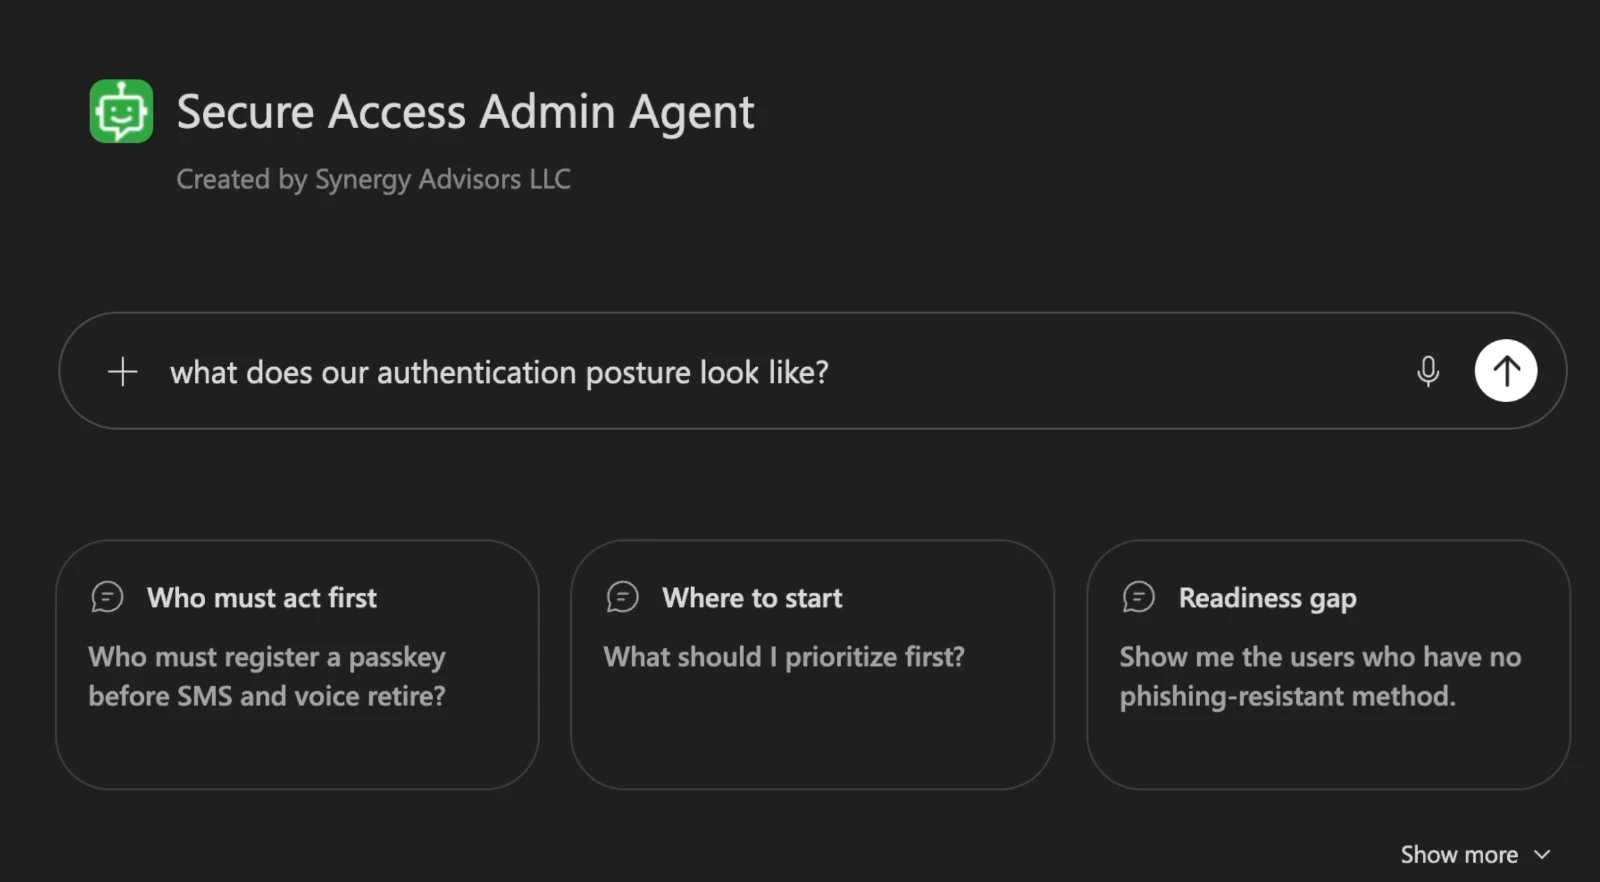
Answers who in your Microsoft Entra ID tenant depends on SMS or voice, who still signs in that way and what to fix first before February 1, 2027.
- Priorities ranked by deadline and impact
- Phishing-resistant adoption in real numbers
- Read-only, in your own tenant
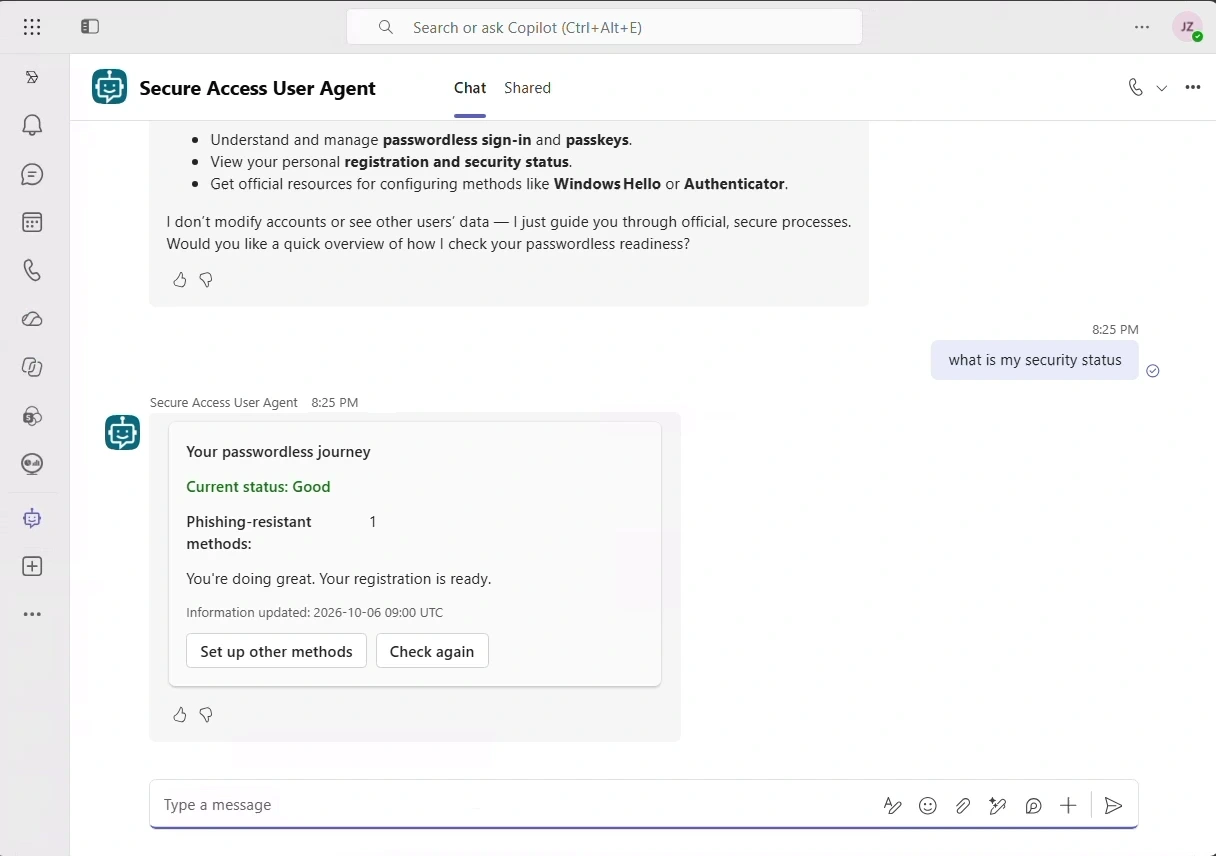
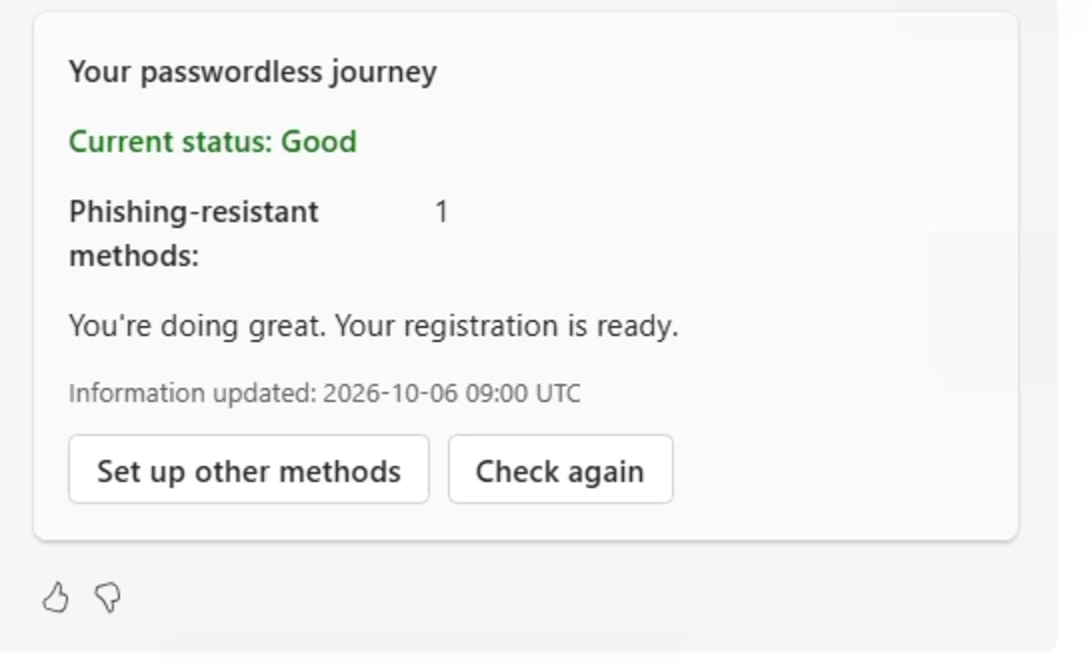
Runs your passkey campaign inside Microsoft Teams: it shows each person their own status, explains the change in plain language and guides them to register a passkey.
- A personal status card in Teams
- Clear answers about passkeys
- Guided registration at aka.ms/mysecurityinfo
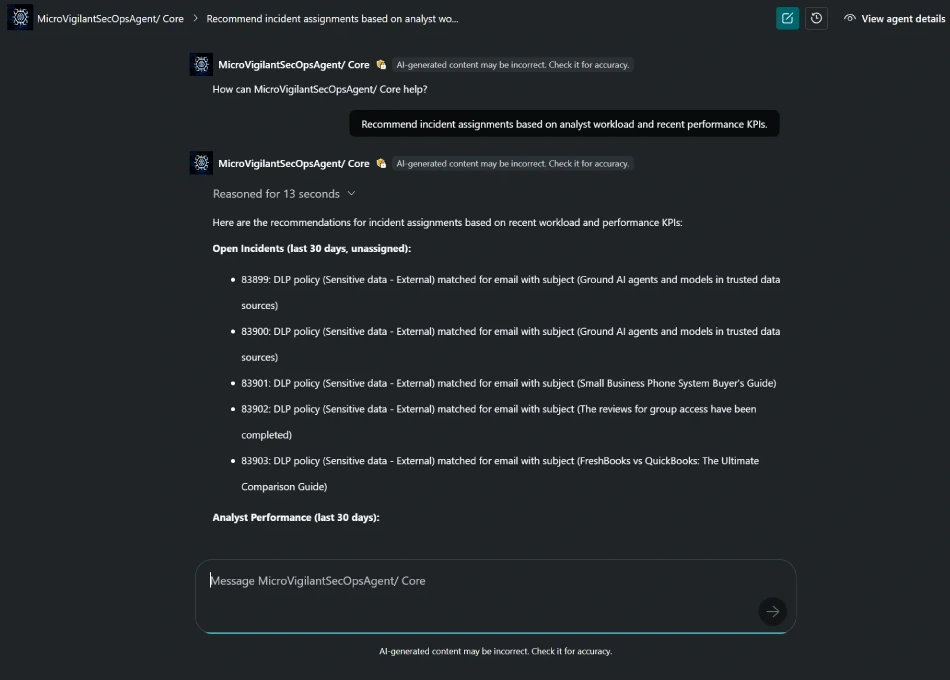
Turns Microsoft Defender XDR operational data into insights for SOC teams: operational health, analyst workload, critical incidents and detection quality.
- SOC health, stale and unassigned incidents
- Analyst workload and mean time to resolution
- Available in the Microsoft Security Store
Find the right E-gent for your team
Tell us about your environment. A Synergy Advisors specialist will show you the agents on the scenarios that matter to you.
Share your contextYour environment, licensing and priorities.
See the agents workingA demo on the scenarios that matter to your team.
Get startedIn English or Spanish, with our experts alongside you.